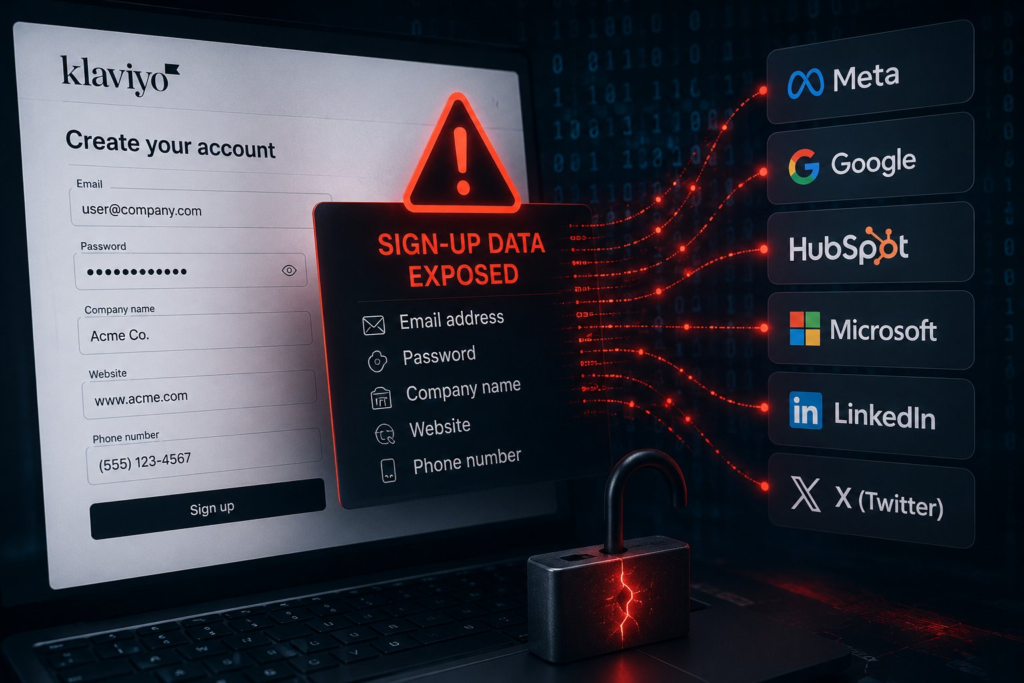
Klaviyo has fixed a website configuration bug that may have exposed new customers’ sign-up data, including passwords, to third-party trackers embedded on its site.
The company says fewer than 200 people are known to have been affected based on its readily available active logs. That figure is not a final total, because Klaviyo has not said how far back those logs extend or exactly how long the misconfiguration remained live.
What the Klaviyo sign-up bug may have exposed
TechCrunch reported that security researcher Sam Jadali, co-founder of Melurna, found the Klaviyo sign-up form was misconfigured from at least February 2024 through November…
Read the full article at TECHREPUBLIC.COM