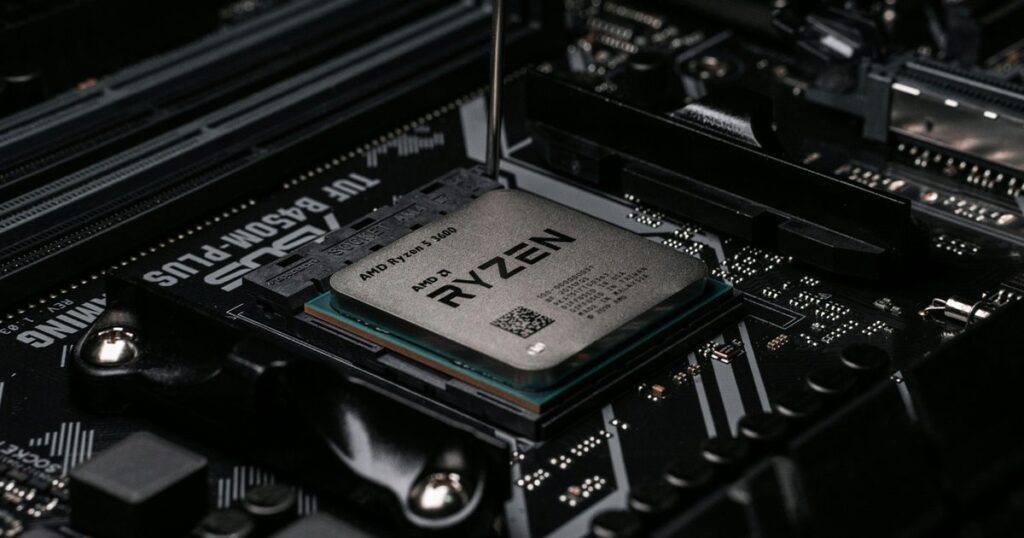
Spectre has been haunting CPU security since 2018, and MIT researchers have now found another way to make it misbehave. The new TONTOU attack can bypass some of the defenses Intel and AMD have added over the years by exploiting a tiny gap in how those protections work. The research comes from Daniël Trujillo and Mengjia Yan at MIT’s Computer Science and Artificial Intelligence Laboratory (CSAIL). Their findings show that even after a processor wipes or isolates information used by its branch predictor, there can be a brief window before that information is actually used. TONTOU, short for Time-of-Neutralization to Time-of-Use, attacks…
Read the full article at DIGITALTRENDS.COM