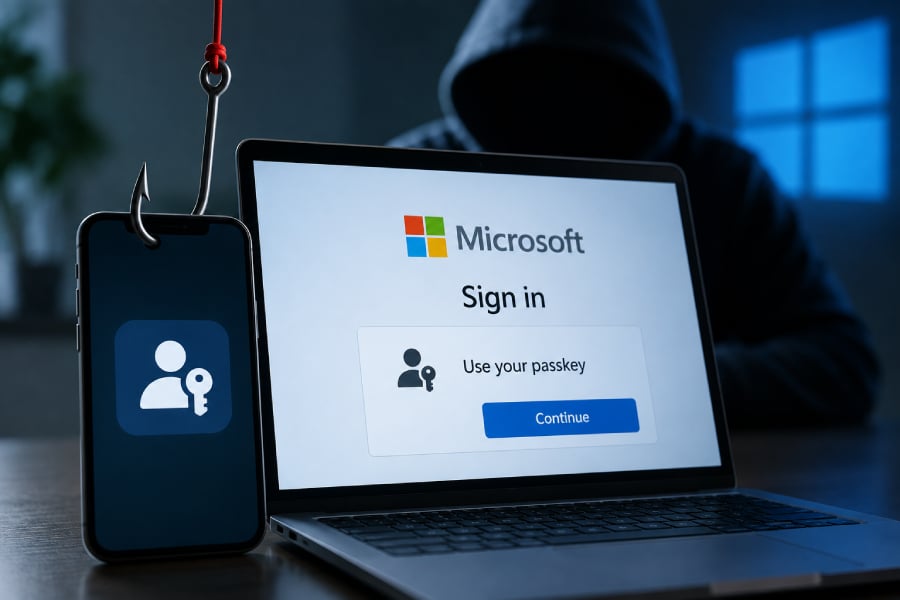
A security feature meant to make Microsoft accounts harder to hijack is becoming the bait attackers use to trick employees into approving the wrong login.
Microsoft researchers have tracked campaigns since May 2026 in which attackers impersonate IT staff and tell employees they need to update a passkey, multifactor authentication, or single sign-on setting. The activity has been linked to multiple threat groups.
Once an account is compromised, Microsoft says the attackers conduct reconnaissance, add authentication methods for persistence, and access data across services including SharePoint, OneDrive, and Exchange Online.
How attackers turn…
Read the full article at TECHREPUBLIC.COM