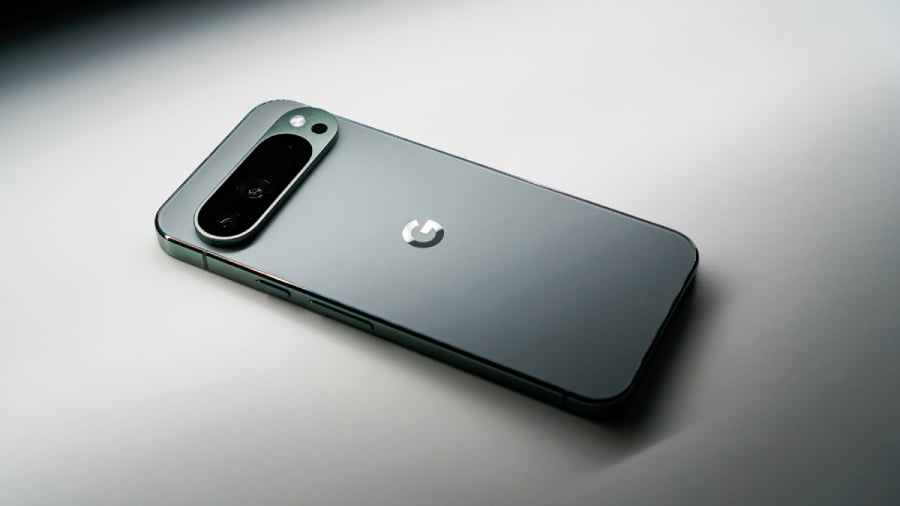
Google disclosed this week that an unknown group of attackers actively weaponized a zero-day security flaw inside the cellular modem of its Pixel smartphones before engineers could fix it.
Tracked as CVE-2026-58704, the high-severity defect allows unauthorized actors to allow an adjacent attacker to escalate privileges without requiring the victim to click a phishing link, download an attachment, or answer a call.
CISA quickly added the flaw to its Known Exploited Vulnerabilities catalog and required affected federal agencies to remediate it within three days.
The Cybersecurity and Infrastructure Security Agency added the vulnerability to its…
Read the full article at TECHREPUBLIC.COM